# Chmod Calculator
Tick the permission boxes or type an octal mode such as 755, and get the chmod command, the ls -l string and a plain-English explanation.
| Class | Read (4) | Write (2) | Execute (1) |
|---|---|---|---|
| Owner (u) | |||
| Group (g) | |||
| Others (o) |
How Linux file permissions work
Every file and directory carries a 12-bit mode. Nine of those bits are the permissions you see every day, split into three classes of three bits each. The other three bits are special flags that we will get to further down.
The three classes are:
- Owner (
u, for user): the account that owns the file. - Group (
g): the one group recorded on the file. - Others (
o): everyone else on the system.
Each class gets three permissions, and each permission has a numeric value:
| Permission | Letter | Value | On a file | On a directory |
|---|---|---|---|---|
| Read | r | 4 | read the contents | list the names inside |
| Write | w | 2 | change the contents | create, rename and delete entries |
| Execute | x | 1 | run it as a program | enter it (cd) and reach files inside by name |
Add the values within a class and you get one octal digit. rwx is 4+2+1 = 7, r-x is 4+1 = 5, rw- is 4+2 = 6, and r-- is 4. Write the three digits in the order owner, group, others and you have the mode: 755 means rwx for the owner and r-x for group and others.
Pick a mode in the calculator above and the checkboxes, the octal field and the ls -l string all change together, so you can learn the mapping by clicking.
What execute means on a directory
Execute on a directory is the part people trip over. Without x you cannot cd into the directory or open anything inside it by path, even if you could read the file itself. Read on a directory only lets you list the names. I made this mistake on purpose in the lab: after running chmod -R 644 site, the directory itself lost its execute bit and even the owner could not reach the files inside.

Directories almost always want x wherever they have r. Remember that and most of the “permission denied” puzzles go away.
Reading ls -l
ls -l prints the type and the nine permission bits as ten characters. The first is the file type (- for a regular file, d for a directory, l for a symlink). The next nine are owner, group and others, three characters each. A dash means the bit is off.
The lab directory below has three files. I used ls -ln here, which prints the numeric user and group IDs (501 and 0) in place of names, so the columns line up the same on any machine:

Reading the first column of each line:
-rw-------is mode 600: the owner reads and writes, nobody else gets anything.-rw-r--r--is mode 644: the owner reads and writes, everyone else reads.-rwxr-xr-xis mode 755: the owner has full access, everyone else reads and executes.
On a normal system ls -l shows the owner and group names instead of the numbers; the permission column is identical.
To print the mode directly as octal, the BSD and macOS stat takes -f:
stat -f '%Sp %Lp %N' notes.txt run.sh id_demo%Sp is the symbolic string, %Lp the octal permission bits, %N the name. On Linux the GNU equivalent is stat -c '%A %a %n' (GNU/Linux syntax, not run here, so no output is shown for it).
Octal versus symbolic mode
chmod accepts two notations and they are interchangeable for the same result.
Octal sets every bit at once: chmod 644 notes.txt. It is short and unambiguous, and it is what most tutorials and config files use.
Symbolic describes a change: who, an operator, and the permissions. The operators are + (add), - (remove) and = (set exactly). Who is a mix of u, g, o or a for all.
chmod u=rwx,g=rx,o= run.shThe line above sets the owner to rwx, the group to r-x and others to nothing, which is exactly chmod 750 run.sh. The calculator prints both forms for whatever mode you choose.

Symbolic mode shines when you want to change one thing without restating the rest. chmod a+x tool.sh adds execute for everyone and leaves read and write alone. chmod go-rwx tool.sh strips everything from group and others.

Use octal when you know the exact end state, symbolic when you want a targeted tweak.
chmod 755
Mode 755 (rwxr-xr-x) is the default for things that run or that people walk into: shell scripts, compiled binaries, web roots, and most directories.
chmod 755 run.shThe owner can edit the file; everybody can run it but nobody else can change it. A script cannot be started as ./run.sh unless it has the execute bit for the user running it. That includes scripts launched by a scheduler: if a cron job fails with “Permission denied”, check x first, and use the cron expression generator to make sure the schedule itself is right. If you run a script through the interpreter (bash run.sh) only the read bit is needed.
chmod 777 and why to avoid it
Mode 777 gives read, write and execute to everyone. It is the most-copied “fix” for permission errors and one of the worst.
The danger is the write bit for others. Any local account, any compromised web app running as www-data, any container sharing the volume can replace the file with something else, and the next time root or a deploy job runs it, that code runs with those privileges. On a web server a 777 upload directory is a classic way to get a web shell.
Here is what 777 does to a tree. I created a small site and applied it recursively:
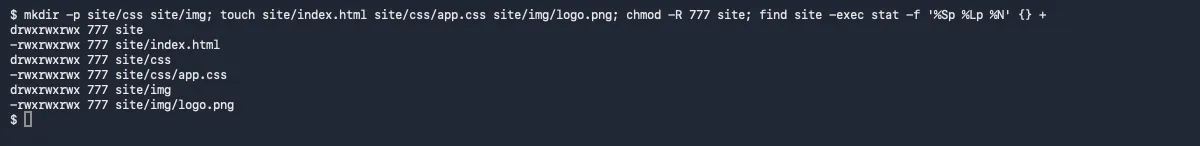
Even the plain HTML and image files now carry execute bits they never needed. What to use instead depends on the actual problem:
- A shared project directory: put collaborators in one group,
chgrpthe directory to it, and use 775 (or 2775 with setgid so new files inherit the group). - A web server that must write uploads: make the server user the owner of that one directory with 755, or 775 with a shared group, never 777.
- A script that “won’t run”: you want
chmod +x, not 777. - A file written by two services: give both the same group and use 664 or 660.
The calculator shows a warning whenever the mode is world-writable, so you can see what you are about to apply.
chmod 644
Mode 644 (rw-r--r--) is the standard for regular files: the owner reads and writes, everyone else reads. It is what HTML, CSS, images, config files and source files should normally have. With the common umask of 022, new files are created as 644 anyway, as the umask section shows below.
chmod 644 notes.txtIf the file holds secrets (a .env, a database password file), 644 is too open. Go to 600 or 640.
chmod 600, SSH keys and 700, 400
Mode 600 (rw-------) means only the owner can read or write. It is the right mode for private keys, credentials and anything personal.
chmod 600 id_demoThis one is not optional for SSH. OpenSSH refuses to use a private key that group or others can read, and prints a warning that the key’s permissions are too open before it gives up. (I did not run an SSH login for this article, so I am describing the behavior rather than pasting its output.) The fix is chmod 600 on the key and chmod 700 on the ~/.ssh directory.
Two quick companions:
- 700 (
rwx------): a private directory only you can enter. Use it for~/.sshand similar. - 400 (
r--------): read-only even for you. Good for a key or certificate you never want to overwrite by accident. You can still change the mode back as owner, and root bypasses it entirely.
chmod recursive (-R)
-R applies the mode to a directory and everything under it:
chmod -R 755 project/The trap is that it treats files and directories the same. A mode good for directories (755, needs x) makes every file executable; a mode good for files (644) removes x from directories and locks you out of them. Mode 777 shown earlier is exactly this problem.
The find pattern
The reliable fix is to pick files and directories separately with find:
find site -type d -exec chmod 755 {} +find site -type f -exec chmod 644 {} +On the 777 tree from before, those two commands give this:
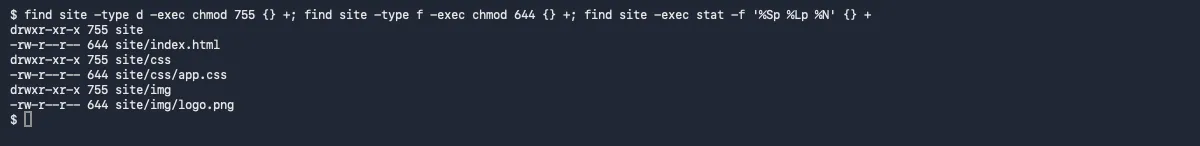
Directories ended at 755 and files at 644, which is what a web root wants. The + at the end batches many paths into one chmod call, which is faster than \;, which runs one process per path.
Capital X
There is a shorter way. In symbolic mode, a capital X means “execute, but only if this is a directory or already has an execute bit for someone”:
chmod -R u+rwX,go+rX siteThat one command restored the directory in the earlier screenshot to drwxr-xr-x, and files without any execute bit stay without one. Build tools use the same idea: the RPM build log in this post on building and signing RPM packages runs chmod -Rf a+rX,u+w,g-w,o-w . on the source tree, the same idiom.
Special bits: setuid, setgid and sticky
A fourth, leading octal digit holds three flags. They are added to the usual three digits, so 4755 is setuid plus 755.
| Bit | Value | On an executable | On a directory |
|---|---|---|---|
| setuid | 4000 | runs as the file’s owner | no effect on Linux |
| setgid | 2000 | runs as the file’s group | new files inherit the directory’s group |
| sticky | 1000 | no practical effect | only the file owner (or directory owner, or root) can delete or rename entries |
In ls -l they take over the execute slot: s in the owner slot for setuid, s in the group slot for setgid, t in the last slot for sticky. A lowercase letter means the execute bit underneath is also set. A capital letter means it is not, which is usually a mistake because the special bit then does nothing useful. I applied five modes to a file in the lab and read them back:
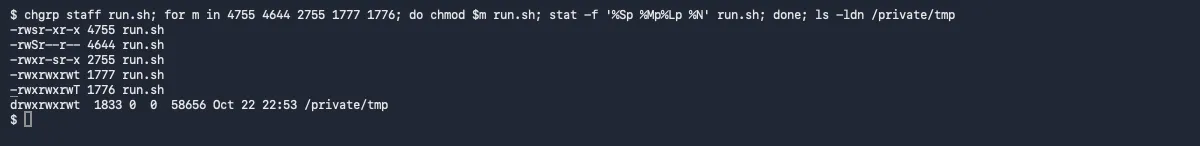
The stat format used here, %Mp%Lp, adds the special bits in front of the three permission digits; plain %Lp would have dropped them. The same strings come out of the calculator: 4755 gives rwsr-xr-x, 4644 gives rwSr--r-- and 1776 ends in a capital T.
The best-known sticky directory is /tmp. Everyone can create files in it, but you cannot delete someone else’s. On this Mac /tmp is only a symlink, and the real directory is /private/tmp:

That drwxrwxrwt is mode 1777: world-writable, made safe by the sticky bit. On Linux /tmp is the real directory with the same mode.
Be careful with setuid. A setuid-root program runs with root’s power no matter who starts it, which is why passwd can edit the password database. Linux ignores setuid on interpreted scripts, and where it is honored it is a well-known hole. The calculator warns you when you combine setuid with a script name such as deploy.sh.
umask: where default modes come from
New files do not start at 777 or 666 and then get chmoded; the shell’s umask removes bits from a starting mode (666 for files, 777 for directories). Here is the lab with the common 022, then with 077 in a subshell:
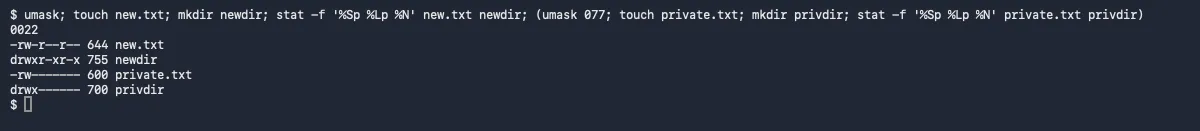
With 022, files come out 644 and directories 755. With 077, only the owner gets anything: 600 and 700. If your own files keep coming out too open or too closed, adjust the umask before reaching for chmod -R.
Common modes at a glance
| Octal | Symbolic | Typical use |
|---|---|---|
| 400 | r-------- | read-only key or certificate |
| 600 | rw------- | private keys, credentials |
| 640 | rw-r----- | config readable by a service group |
| 644 | rw-r--r-- | regular files, web content |
| 664 | rw-rw-r-- | files shared by a group |
| 700 | rwx------ | private directory, ~/.ssh |
| 750 | rwxr-x--- | program or directory for owner and group only |
| 755 | rwxr-xr-x | scripts, binaries, directories |
| 775 | rwxrwxr-x | shared directory with a group |
| 1777 | rwxrwxrwt | world-writable with sticky bit, like /tmp |
| 2775 | rwxrwsr-x | shared directory where new files inherit the group |
| 4755 | rwsr-xr-x | setuid program |
| 777 | rwxrwxrwx | avoid |
Common mistakes
- Using 777 to silence an error. Find out which user needs access and grant exactly that.
chmod -R 755on a tree full of data files. Everything becomes executable. Use thefindpattern or capitalX.chmod -R 644on directories. Withoutxyou cannot enter them, as the screenshot above shows.- Forgetting
xon a script../run.shthen fails with “Permission denied”. - Loose key permissions. SSH keys need 600 and
~/.sshneeds 700. - Confusing chmod and chown. A correct mode on the wrong owner still fails.
- Reading a trailing
.or+inls -l. That marks an SELinux context or an ACL; the mode column alone no longer tells the whole story. - Unquoted paths with spaces or special characters. The calculator quotes the path for you, so
my file.txtbecomes'my file.txt'.
If you work mostly in a terminal, my notes on a terminal setup with iTerm and tmux include the chmod 755 step for a startup script, and the post on a Bash script that builds a tmux environment is a good example of a script that needs its execute bit.
Frequently asked questions
What does chmod 755 mean?
The owner can read, write and execute (7 = 4+2+1). The group and everyone else can read and execute (5 = 4+1) but not write. It is the usual mode for programs, scripts and directories that others need to enter or run.
Is chmod 777 ever safe?
Almost never. It lets every user and every process on the machine modify and replace the file. Work out which user or group actually needs access and grant that instead, for example 775 with a shared group, or 755 with the right owner.
What is the difference between chmod 644 and chmod 664?
Both let the owner read and write and everyone else read. 664 also lets the group write, which is useful for a shared project directory where collaborators belong to one group. If nobody besides the owner should edit the file, use 644.
How do I chmod only files or only directories recursively?
Use find: find . -type d -exec chmod 755 {} + for directories and find . -type f -exec chmod 644 {} + for files. Or use a symbolic mode with capital X, which adds execute only to directories and files that already have an execute bit: chmod -R u+rwX,go+rX .
Why does ssh say my private key permissions are too open?
OpenSSH refuses to use a private key that other users can read. Set it to 600 (or 400) with chmod 600 ~/.ssh/id_ed25519, and keep the ~/.ssh directory itself at 700.
What do the s and t in ls -l output mean?
A lowercase s in the owner or group execute slot means setuid or setgid is set together with execute. A t in the last slot is the sticky bit. A capital S or T means the special bit is set but the matching execute bit is not, which is almost always a mistake.
What is the difference between chmod and chown?
chmod changes what the owner, group and others may do. chown changes who the owner and group are. A file can be perfectly chmoded and still unreachable because it is owned by the wrong user.
Why do I get Operation not permitted when I run chmod?
Only the file owner or root can change a mode. If you own the file and still see the error, check for immutable flags, a read-only filesystem, or (for setgid) whether you actually belong to the file's group.