GeekCoding101
STRIDE threat modeling is a way to find security flaws at design time. You check every part of a system against six threat categories: Spoofing, Tampering, Repudiation, Information disclosure, Denial of service and Elevation of privilege. Each category breaks one security property, so working through all six gives you a structured answer to “what could go wrong here?” before an attacker answers it for you.
In this post I’ll apply STRIDE to a deliberately simple chat app. For each threat you’ll see what it means, how it shows up in the app, how to detect it and how to prevent it.
Info: Check out the one-page Threat Modeling Manifesto. It’s a short, sharp read on why threat modeling matters.
STRIDE at a glance
| Letter | Threat | Security property it violates | Typical question |
|---|---|---|---|
| S | Spoofing | Authentication | Can someone pretend to be another user or system? |
| T | Tampering | Integrity | Can someone change data or code they shouldn’t? |
| R | Repudiation | Non-repudiation | Can someone do something and deny it later? |
| I | Information disclosure | Confidentiality | Can data leak to someone who shouldn’t see it? |
| D | Denial of service | Availability | Can someone make the system slow or unusable? |
| E | Elevation of privilege | Authorization | Can someone gain rights they weren’t given? |
Why every app needs threat modeling, and why STRIDE
I’ve been meaning to write this post for a long time. STRIDE isn’t the hottest buzzword in cybersecurity, and threat modeling isn’t some shiny new technique. I’m writing it because if you’re building or defending any system, threat modeling is non-negotiable. That includes something as deceptively simple as a chat app.
Maybe you’re knee-deep in SecOps, defining IAM policies, tuning your SIEM or crafting detection logic. Either way you have one mission: protect the stuff that matters. That means user data, privacy, service uptime and reputation. If we don’t design with threats in mind, we’re just building breach bait with good intentions.
So why STRIDE? It gives you a practical lens on risk before the attacker gets there. You don’t have to wait and react to CVEs or chase zero-days. STRIDE makes you think like a malicious actor while you’re still sketching the architecture on a whiteboard or writing that controller code.
Our target: a chat app
Let’s keep it humble. No machine learning, no blockchain, no AI buzzwords glued onto CRUD. Just a straightforward web-based chat application:
- User registration: email + password
- Login system: username/password auth, session cookies
- User directory: displays online users
- 1:1 messaging: users can send and receive messages
- Message history: stored and retrievable
- Admin panel: hidden route, unknown to regular users
This setup probably feels familiar. It’s the backbone of a thousand hackathons and product MVPs. But simple apps are hacker candy, because developers keep making the same assumptions:
- “It’s just a prototype.”
- “Who would even try to attack this?”
- “We’ll add security later.”
Later never comes. These “low-risk” features can become pivot points for privilege escalation, data leaks or full compromise. One misconfigured route or weak endpoint can become your next incident report ticket.
So before we start breaking things in Part 2, let’s map out what could go wrong.
Where STRIDE came from, and the tools that support it
A short history
STRIDE was created at Microsoft by Loren Kohnfelder and Praerit Garg in the late 1990s. Microsoft later built it into the Security Development Lifecycle (SDL) during its Trustworthy Computing push in the early 2000s. Yes, that was the era when Windows XP was everyone’s favorite backdoor. 😅
The goal was to give developers and architects a lightweight, repeatable way to ask “What could go wrong here?” Teams had been tossing in a firewall and calling it a day. STRIDE made them think in threat categories, not just patches and alerts.
It still holds up, especially in a world of microservices, APIs, cloud platforms and third-party integrations.
Tools that support STRIDE
You don’t have to scribble on napkins (though respect if you do). These tools help you bring STRIDE into your workflow:
| Tool | Description | Good for |
|---|---|---|
| OWASP Threat Dragon | Open-source threat modeling tool with STRIDE support | Visual modeling, diagrams |
| Microsoft Threat Modeling Tool | Free tool from Microsoft for STRIDE-based modeling | STRIDE templates, data flow diagrams |
| IriusRisk | Commercial platform for automated threat modeling and compliance mapping | Enterprise threat modeling at scale |
| Draw.io + STRIDE cards | DIY visual modeling with STRIDE cards (for example, the Elevation of Privilege card game) | Lightweight teams, whiteboard replacement |
Pro tip: If you already draw architecture diagrams in a tool like Lucidchart or Miro, just layer STRIDE annotations on top. It’s easier than adopting a whole new platform.
STRIDE breakdown: mapping threats to the chat app
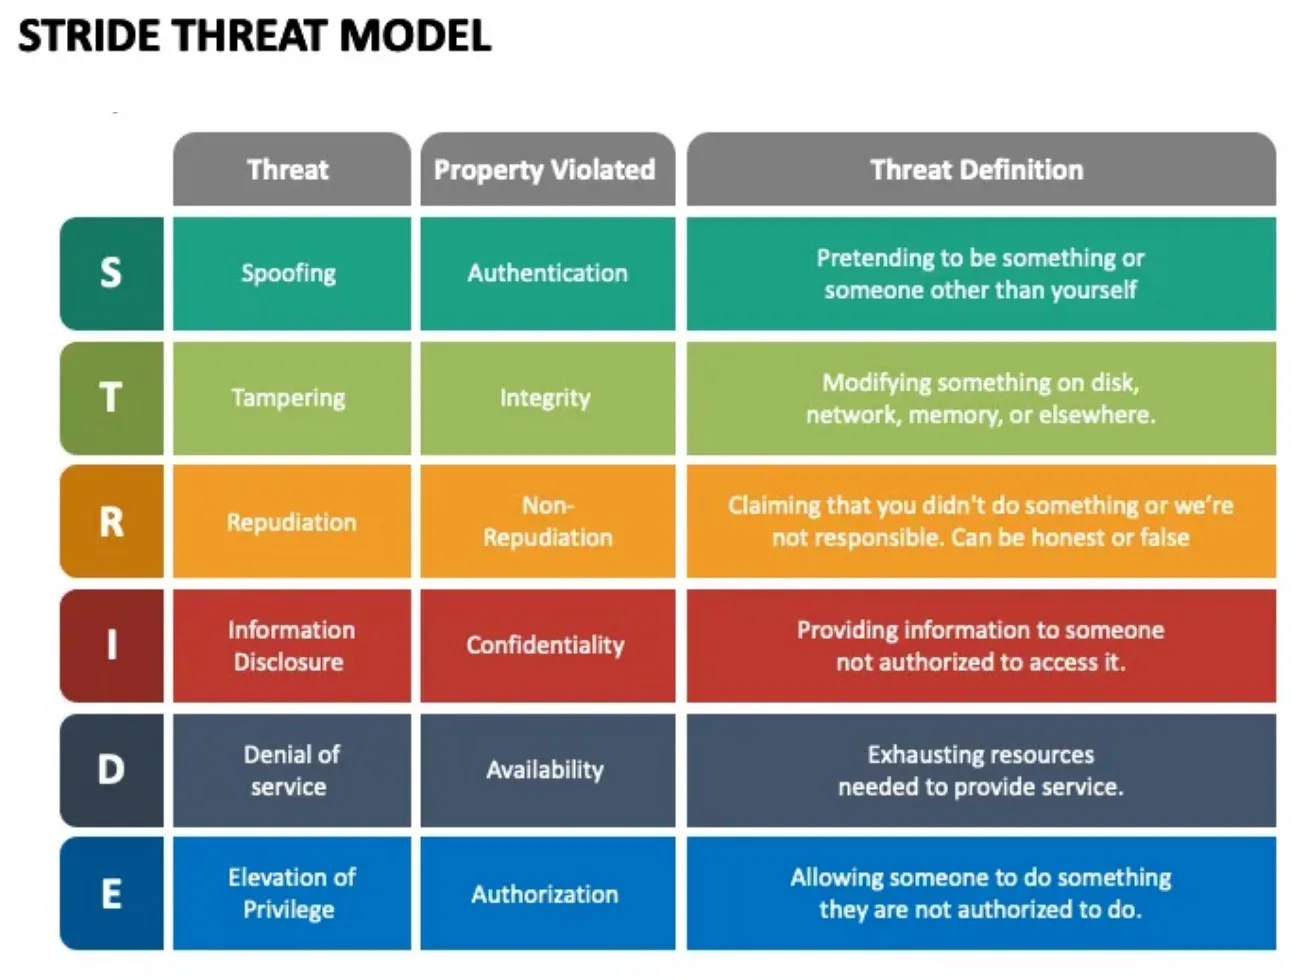
For each category we’ll look at:
- What it means
- Real-world relevance
- How it applies to our chat app
- How to detect it
- How to prevent or mitigate it
Let’s dive in.
S – Spoofing identity
What it means
Spoofing is pretending to be someone you’re not. It usually means faking an identity through unauthorized logins, session impersonation or token theft. It doesn’t have to be high-tech. A weak password policy or default admin credentials are all it takes.
Real-world relevance
- Credential stuffing from leaked password dumps
- Session hijacking via stolen cookies
- Social engineering that leads to unauthorized access
Chat app example
- An attacker tries logging in as
adminwith common passwords likeadmin123orpassword. - The registration page says “User already exists”, which lets an attacker confirm valid accounts.
- The session cookie lacks the
HttpOnlyandSecureflags. An attacker who gets JavaScript onto the page can read and steal the session.
How to detect
- Unusual login attempts across many usernames
- Brute-force behavior from single IPs
- One session reused across different IPs or devices
How to prevent
- Enforce strong passwords and rate limiting on login
- Use MFA (seriously, just do it)
- Harden sessions with
HttpOnly,SecureandSameSite=Strict - Return generic error messages (“Login failed”) on login and registration to prevent account enumeration
- Alert on login anomalies, such as geolocation or timing mismatches
T – Tampering with data
What it means
Tampering is unauthorized modification of data. Examples include altering messages, changing user roles or injecting parameters to mess with system behavior. It can happen at rest (modifying database records), in transit (man-in-the-middle) or through insecure APIs.
Real-world relevance
- Changing prices on e-commerce sites
- Modifying permissions via API parameter injection
- Overwriting user data through insecure endpoints
Chat app example
- A user crafts a
PUT /api/messages/1234call to edit someone else’s message. - A user sends a chat message with an embedded
<script>tag that runs in the recipient’s browser. - A user edits role data stored in
localStorageto changeusertoadmin, and the app trusts it.
How to detect
- Unexpected mutations in data logs
- Role changes or message edits by users who shouldn’t be able to make them
- Parameter tampering attempts flagged by your WAF or API gateway
How to prevent
- Enforce authorization checks on the server, not just in the UI
- Use TLS everywhere to protect data in transit
- Use signatures or MACs (for example, HMAC) where message integrity must be verifiable
- Validate input and encode output so user content can’t run as script
- Never trust the client for roles or permissions
R – Repudiation
What it means
Repudiation is when someone performs an action without accountability and then denies it. If the system doesn’t log properly, they get away clean. It’s like someone deleting all your Slack messages and saying, “Wasn’t me.”
Real-world relevance
- Missing logs because of cloud misconfigurations
- Insiders covering their tracks
- Attackers disabling or deleting logs after a compromise
Chat app example
- A user deletes messages and there’s no audit trail of who said what.
- An admin bans a user, but there’s no timestamp or log of that action.
- A rogue employee reads DMs, and no one knows because access wasn’t logged.
How to detect
- Honestly, you can’t, unless good logging was already in place
- Look for missing data or gaps in activity logs
- Use an external system (like a SIEM) to flag deletions or logging gaps
How to prevent
- Use immutable logging, such as append-only logs with checksum verification
- Log every sensitive action: logins, deletions, permission changes, admin actions
- Store logs off-host with centralized logging (for example, ELK or Loki)
- Include a timestamp and user context in every log event
I – Information disclosure
What it means
Information disclosure means data leaks to users who shouldn’t see it. That data could be PII, secrets, internal APIs, or error messages that give away the goods. It doesn’t take a SQL injection. Sometimes it’s just poorly scoped permissions.
Real-world relevance
- Publicly readable cloud storage buckets
- Leaky APIs exposing internal user info
- Stack traces returned in production
Chat app example
- A user calls
/api/messages?id=4001and gets another user’s message, because there’s no ownership check. - The API returns full user records, including emails and IP addresses.
- An error page reveals server paths or the tech stack through a verbose stack trace.
How to detect
- Watch outbound logs for data leaks
- Use DLP (data loss prevention) tools to spot sensitive data patterns
- Review access control on every endpoint and API
How to prevent
- Apply object-level access control and check ownership, not just “is logged in”
- Return only the fields the client needs and strip metadata
- Mask sensitive data (show part of an email, not all of it)
- Disable detailed errors in production
D – Denial of service (DoS)
What it means
DoS means making a system unavailable or unusable, usually by overwhelming it. It can be intentional or accidental. It isn’t only traffic floods. It also covers logic bombs, resource exhaustion and malformed input that crashes the app.
Real-world relevance
- Spamming forms or chat endpoints
- Flooding chat with emojis or huge payloads
- Abusing deeply nested JSON to crash parsers
Chat app example
- A bot sends thousands of messages per second and maxes out the server CPU.
- Large message payloads (10 MB+ text blobs) crash the database or the front end.
- Emoji reactions are abused to spam notifications.
How to detect
- Rate spikes on endpoints (monitor requests per second and latency)
- Alerts for memory, CPU or queue overflows
- App crashes tied to malformed input
How to prevent
- Rate limit per IP, token or user (for example, token buckets in Redis)
- Set a maximum request body size
- Use queue-based processing to isolate spikes from core logic
- Add CAPTCHAs to forms and registration
E – Elevation of privilege
What it means
This one’s the crown jewel of attacks. Elevation of privilege (EoP) is when a normal user gains higher privileges, such as becoming an admin, acting as other users or reaching restricted areas. It usually comes from missing authorization checks or trusting the client.
Real-world relevance
- IDOR (insecure direct object reference)
- Hidden admin features found by poking at URLs
- JWT manipulation (changing
role: usertorole: admin)
Chat app example
- A regular user discovers the
/admin/usersroute and sees the admin dashboard. - The API lets any authenticated user call
DELETE /users/{id}without a role check. - The server accepts unsigned JWTs (
alg: none) or signs tokens with a weak, guessable secret. An attacker forges a valid “admin” token.
How to detect
- Requests to admin-only routes from non-admin accounts
- Spikes in 401/403 responses or failed token signature checks
- Unexpected role or permission changes in audit logs
How to prevent
- Check authorization on the server for every request, and deny by default
- Never rely on a “hidden” route. Obscurity is not access control
- Verify JWT signatures with a strong key and a fixed, expected algorithm. Reject
alg: none - Apply least privilege to users, service accounts and admin tools
- Log and alert on every privilege change (this ties back to Repudiation)
STRIDE’s secret superpower: STRIDE per element
STRIDE gets much more useful when you apply it to a data flow diagram (DFD) instead of the app as a whole. This approach is often called STRIDE per element. Each DFD element type is mainly exposed to certain categories:
| DFD element | Chat app example | STRIDE categories to check |
|---|---|---|
| External entity | User’s browser, admin | S, R |
| Process | Auth service, message API | S, T, R, I, D, E |
| Data flow | Browser → API, API → database | T, I, D |
| Data store | Users table, message history | T, I, D (plus R if it holds logs) |
A lightweight way to run a session:
- Draw the system. Sketch a DFD with users, services, data stores and the flows between them. Mark trust boundaries such as browser ↔ server and app ↔ database.
- Walk each element. Ask the relevant STRIDE questions from the table above.
- Write down threats. One line each: what could happen, where, and what it would break.
- Decide on a response. Mitigate, accept, transfer or eliminate the feature.
- Revisit the model. Update it when the design changes: a new endpoint, a new integration, a new data store.
Final thoughts on STRIDE threat modeling
Our “simple” chat app had a credible threat in every one of the six categories, before we wrote a single exploit. That’s the point of STRIDE. It turns a vague “is this secure?” into six concrete questions you can ask at the whiteboard, in a design review or while writing that controller code.
In Part 2 we’ll stop modeling and start breaking things.
FAQ
What does STRIDE stand for? Spoofing, Tampering, Repudiation, Information disclosure, Denial of service and Elevation of privilege. Each one maps to a security property: authentication, integrity, non-repudiation, confidentiality, availability and authorization.
Who created STRIDE? It came out of Microsoft, created by Loren Kohnfelder and Praerit Garg. It later became part of the Microsoft Security Development Lifecycle (SDL).
When should you do STRIDE threat modeling? As early as possible, ideally while the architecture is still on the whiteboard. Repeat it whenever the design changes. Fixing a design flaw before it ships is far cheaper than patching it after an incident.
What’s the difference between STRIDE and DREAD? STRIDE helps you find and classify threats. DREAD is a scheme for rating how serious a threat is. Many teams pair STRIDE with a separate risk-rating method to prioritize fixes.
Is STRIDE still relevant today? Yes. The six categories describe kinds of failure, not specific technologies, so they apply just as well to microservices, APIs, cloud platforms and third-party integrations as to classic web apps.